Security and Control Design
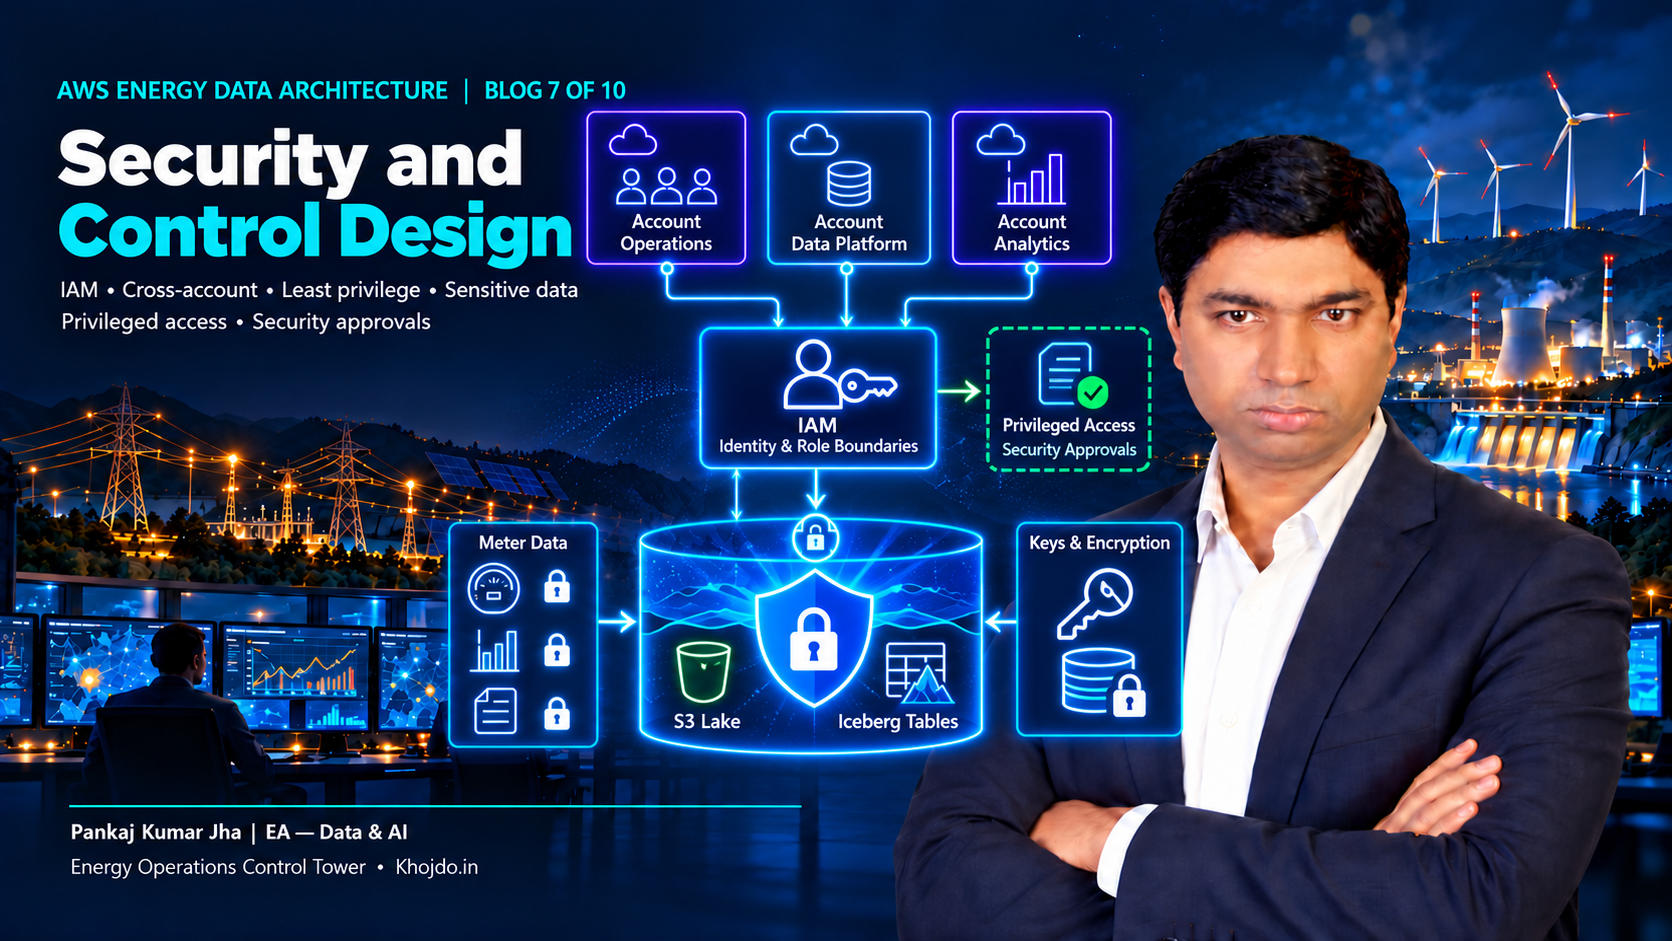
A practical AWS security design for an energy data platform, covering workforce and workload identities, cross-account data sharing, least privilege, sensitive data, privileged access and security approvals.
AWS Energy Data Architecture | Blog 7 of 10
Security and Control Design: IAM, Cross-Account Access, Least Privilege and Sensitive DataBy Pankaj Kumar Jha | EA — Data & AI
Running example: An energy operations control tower with generation, smart-meter, asset, weather and market data. The same controls apply to financial-markets data, with client-specific regulatory, confidentiality and audit requirements.
Every identity, data path and elevated action should have a clear owner and purpose.Scenario: The data platform spans separate AWS accounts for security, logging, shared platform services, development and production. Domain teams publish Iceberg tables to Amazon S3, while analysts, engineers and dashboards access approved data. The design must protect sensitive information, support cross-account collaboration, and provide controlled access for emergency operations.
Create a free account to read the rest
This article is open to registered readers. Signing up takes a minute and costs nothing.